AI Governance | Risk Management


HITRUST & AI Solutions
AI Risk Management
Assessment
51
Controls
- Aligned with NIST AI RMF + ISO/IEC 23894:2023
- Identify gaps and prioritize actions
- Non-certified; focused on improving AI risk posture
AI Security Assessment
& Certification
44
Requirements
- Formal HITRUST AI Security Certification
- Standalone or paired with HITRUST e1/i1/r2
- Designed for AI platforms, developers and deployers
AI Penetration Test
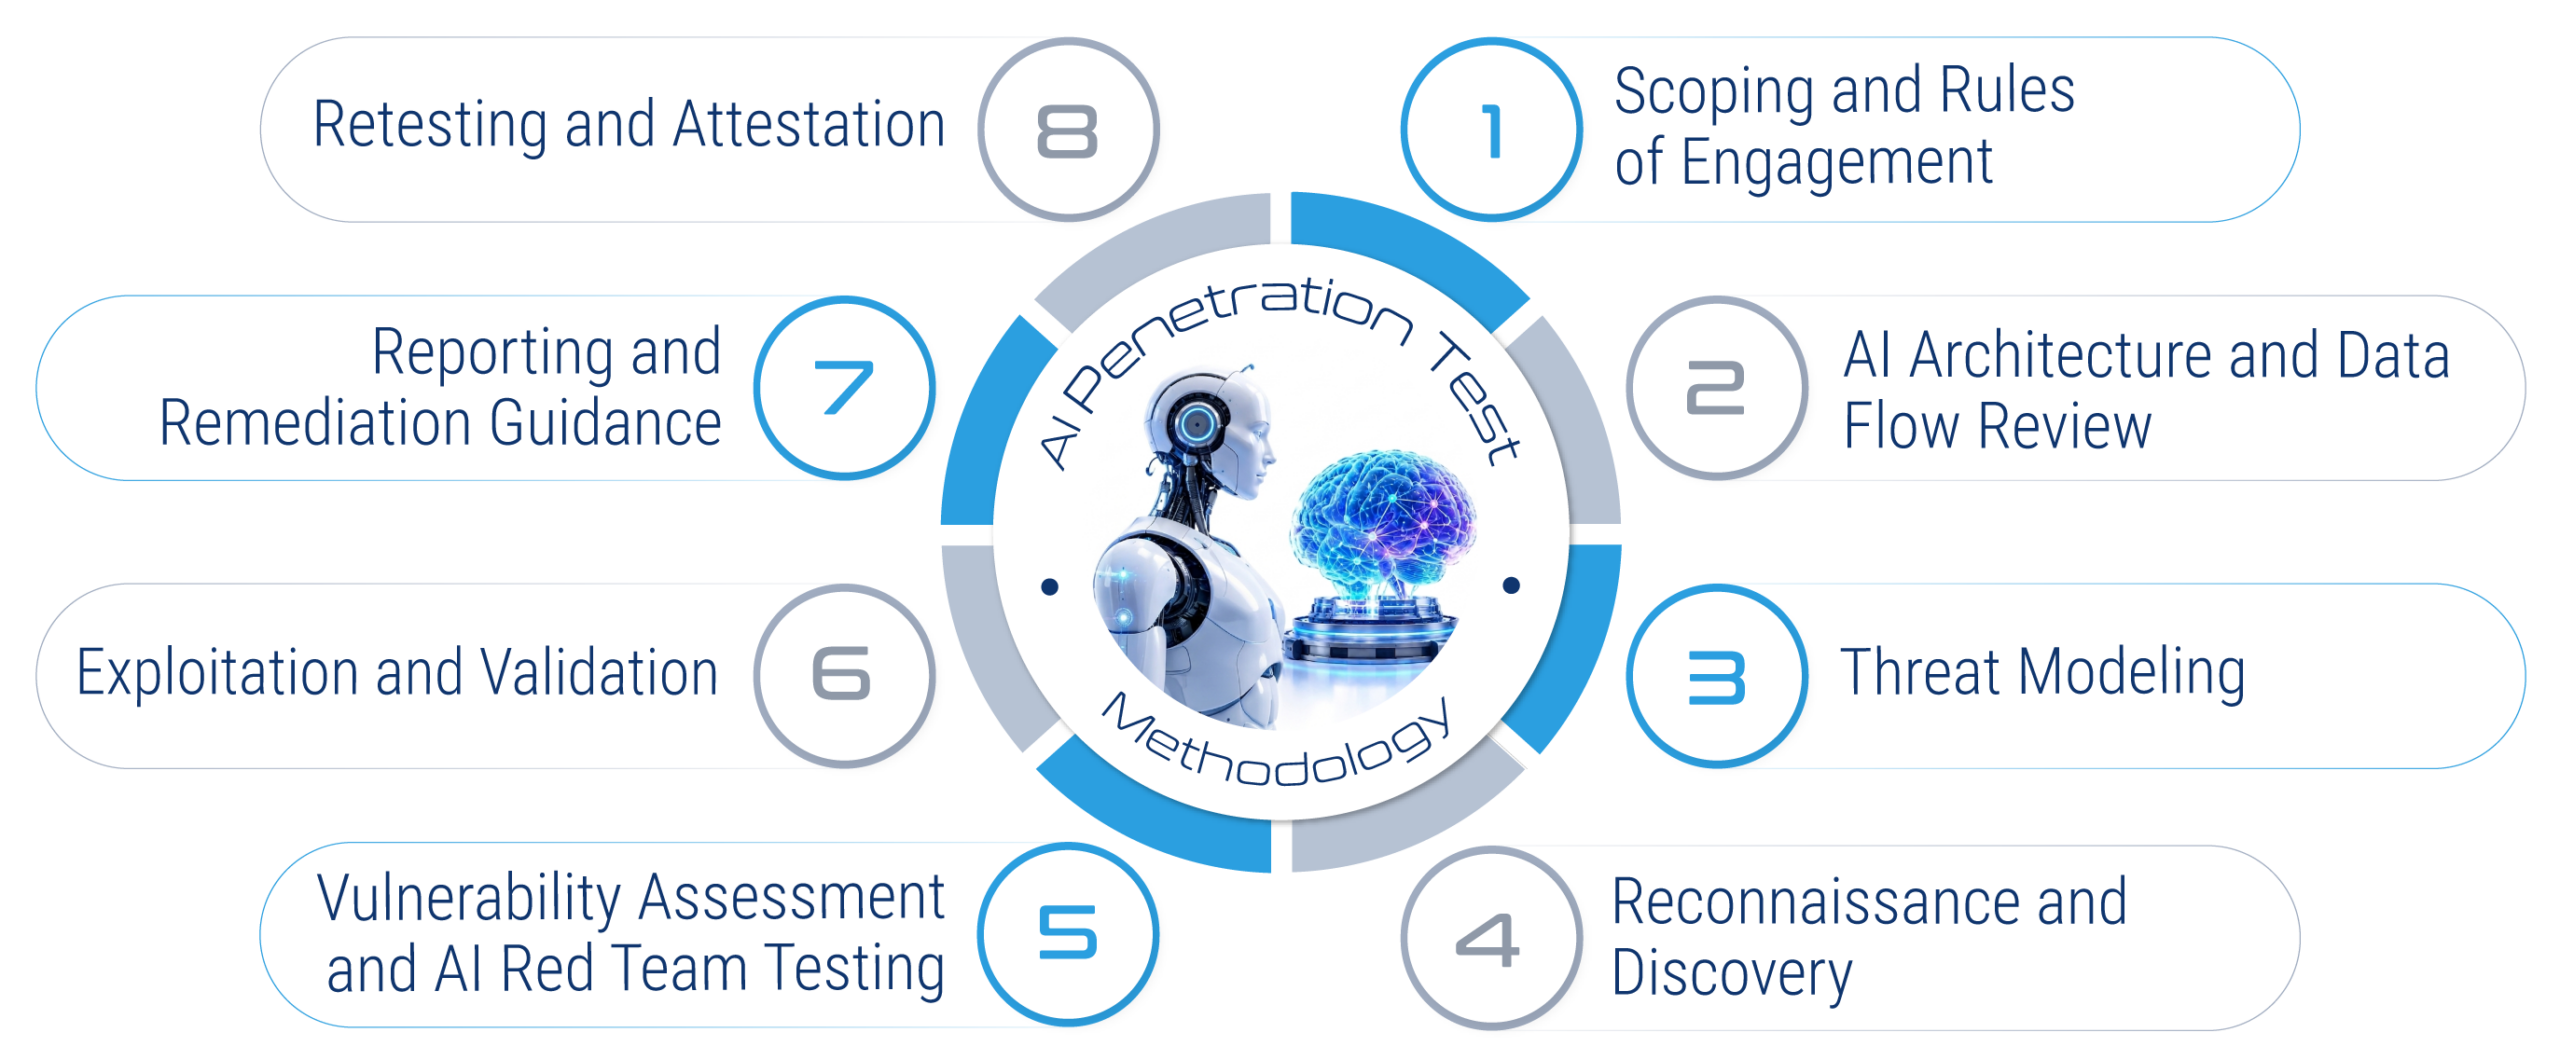
-
 Your AI Attack
Surface -
 Customized
Approach -
 Our
Methodology -
 Executive
Dashboard
AI Governance Program

- Establish AI governance priorites
- Identify relevant and applicable AI risk management mandates
- Craft a robust AI strategy

- Define AI scope and objectives
- Establish AI roles and responsibilities for oversight and management
- Develop AI risk management assessment objectives

- Align AI risk assessment with applicable global mandates
- Identify AI risk compliance gaps
- Remediate and mitigate AI risk gaps

Learning Objectives
- Examine the NIST AI Risk Management Framework (RMF).
- Review valued AI resources for risk management including ISO 23894 and ISO 42001.
- Understand the European Union AI Act requirements and risk classification areas.
- Step through a sample AI risk management policy.
- Identify AI cyber defense controls.
- Determine key phases for an enterprise AI risk assessment exercise.